Your binder is a working document. We keep its pages on our servers so you can read them anywhere, and so the people you name can read them when it matters.
Sealed details are planned for Family, our paid plan, and are not available yet.
Stored so we can show them to you anywhere, and to the people you name when it matters.
Your sealed envelopes, once Family arrives.
We will store and deliver them still closed. We will not be able to open them.
Your account email, sign‑in state, and billing references.
Stripe holds the card itself.
The names and contact details of the people you choose.
So we can deliver the share link if and when it’s needed.
A record of shares and edits.
When something changed and who it went to; the record itself carries no contents.
The pledge
We cannot read sealed details.
The details you seal will be closed on your device, before they ever reach us.
The keys that open them will never reach us.
This is how they will work when Family arrives.
We cannot read
The three details you seal.
Your phone passcode, your primary email password and your password manager’s master password.
Your backup code.
It will be made on your device and saved by you, somewhere we’ve never been.
The keys that open a sealed envelope.
Your device will hold yours. The people you name will hold theirs. We won’t.
Two ways in: your phone, or the backup code.
The pages of your binder open with an ordinary sign‑in. The sealed envelope will ask for
more: one of two doors. The second will never be optional, because the first one fits in
your pocket and pockets get lost. Both doors will open the same envelope, and there will
never be a second copy of what you sealed.
Door one
The phone in your hand.
When you reach for a sealed detail, your device will prove it’s yours the same way it
unlocks your banking app: your face, your fingerprint, the passcode it already trusts.
From that, the envelope will open.
The proof will never leave the device. We will see only that the door was opened, not the
key that opened it.
or
Door two
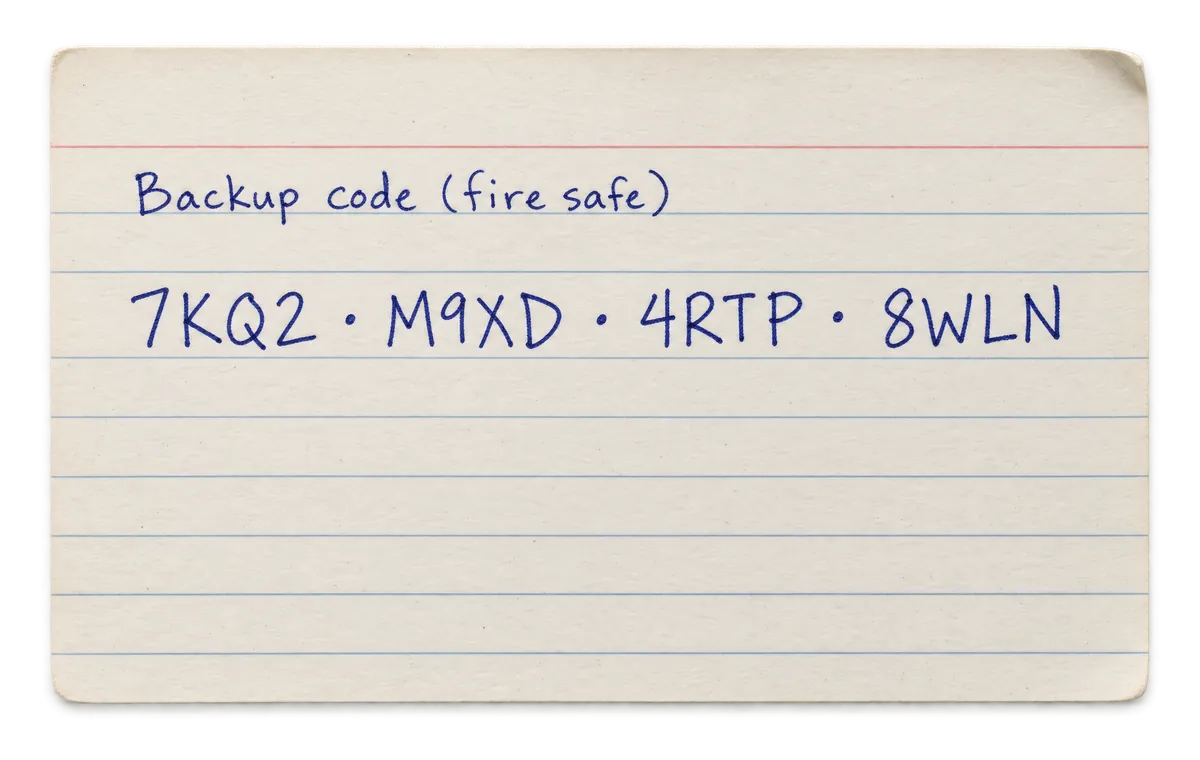
A backup code, written down.
On the day you sign up, Afterward will generate a backup code and ask you to save it
somewhere private: a safe, a wallet pocket, an envelope tucked inside a book.
That code will be the second way in. It will open the same sealed envelope if your phone
is ever lost, broken, or replaced. We will not know what it is.
When something goes wrong.
If you lose your phone
The pages of your binder come back the moment you sign in again. They were never locked to
the phone.
The sealed envelope will ask for the second door: you will enter your backup code, the
whole code will be checked, and the new device will be added as another way in.
Example · fictional details
If you lose the backup code too
We won’t be able to open a sealed envelope for you. Not because we would refuse: each
envelope will be closed on your device, and the means to open it will never reach us. Your
pages will still be here, but what you sealed would need to be sealed again, fresh, on a
device you trust.
This is a trade-off we made deliberately. Every product that promises a way back in for the
forgetful holds the means to read your most sensitive details on an ordinary day. We don’t
want to.
If you stop signing in for a while
The check‑in will come later. Today Afterward sends no 60‑day check‑in and opens no release
window, so a link goes out only when you send it.
What we protect against, and what we don’t.
Read this before you trust us with anything.
We protect
Your sealed details, in a breach of our servers.
An attacker would find your sealed envelopes exactly as we will hold them: closed. Opening one will take keys that never reach us.
Someone at Afterward opening a sealed envelope.
Once sealed details arrive, no one at Afterward will be able to read one: no employee, no founder, no engineer.
Losing your phone.
Your pages come back the moment you sign in again. The sealed envelope will open on a new device with the backup code you saved.
We can’t protect
Your binder pages, in a breach of our servers.
Pages are guarded the way careful services guard data: locked doors, narrow access, a record of who entered. But they are not sealed the way sealed details will be. That difference is why the three most dangerous details will get the envelope.
Someone at Afterward reading a binder page.
Access to production systems is restricted to the few who run them, and it leaves a trail. That is discipline and audit, not mathematics: the difference between a page and a sealed envelope.
Your device being read while it is unlocked.
If someone is using your phone while you’re signed in, we can’t tell the difference between you and them. Your phone passcode is your last line.
Sharing your backup code with the wrong person.
The code will open what you sealed. Anyone holding it will hold that door. We will say so on the day you make it.
A determined attacker watching your screen.
No technology fixes shoulder-surfing. What the binder shows you is still yours to handle with care.
If you leave.
No plan takes your binder away.At any time, on any plan, you can download the printed copy or a portable archive:
every page, in plain files your family could read without our help, without our
software, without us.
The sealed envelopes will be the one thing an export leaves out, on purpose.Sealed details will never travel in a file; they will have their own reveal-and-print
flow, made for paper you keep somewhere safe, one detail at a time.
Who checks our work.
There are no badges here yet. This is the schedule instead.
Selecting
Independent security review
A specialist firm will review the sealed-envelope architecture and the backup-code path before launch. Selection is in progress; the public summary will be linked from this page once the engagement begins.
Engagement · pre-launch
Planned
Penetration testing
We plan an external pen test before each named release, and an annual full-scope test. Findings will go to the engineering team, and to a public changelog once they are fixed.
Intended cadence · per release + annual
In draft
Security whitepaper
A public, plain-language description of the sealed-envelope architecture, recovery model, and threat boundaries. This is the document a security-minded reader can hold us to: the claims on this page, written down precisely.
Publishing · at launch
The architecture, in technical terms.
Where the line sits
Your binder’s pages (the section fields, the contact details, the where-things-are) are stored on our servers as structured records, so we can render them to you and to the people you name. Exactly three details are different in kind: your phone passcode, your primary email password, and your password manager’s master password. Those will be sealed on your device, and the rest of this ledger is about them.
The sealed-details key
A long random key will be created on your device. It will seal the three details, and only those. The key itself will never leave your device for our servers: not at setup, not ever.
First way in
Your device will prove itself the same way it unlocks your banking app. The proof will be converted into a wrapping that holds the sealed-details key. We will see only that the proof checked out, not the proof itself, and the wrapping will never leave your device unsealed. Adding a second device will wrap the same key again, so we will never have to re-seal what you already closed.
Second way in
A backup code, generated on your device, will be run through a slow, memory-hard derivation to produce a second wrapping for the same key. This path will be mandatory: sealed details will not open for the first time until the code exists and you have acknowledged putting it somewhere private.
Sealed envelopes
For each of the three sealed details, an envelope will be sealed against the named recipient’s public key on your device. The sealed envelope will be opaque to us. Only the recipient’s device, holding the matching private key, will be able to open it.
Server boundary
Our servers store binder pages as records, and account metadata; sealed details will be stored as opaque ciphertext beside their wrapped keys. Route handlers never have access to an owner’s private keys, and the sealed tables will hold ciphertext and nonces only, a boundary enforced in code review on every change that touches it.
Recovery from a single device
Lose the phone, sign in with the backup code, enroll the new device, and the sealed-details key will be re-wrapped for it. Lose both the phone and the code, and the sealed details will be unrecoverable by design: your pages remain with your account, but what you sealed must be sealed again. This is the same trade-off Bitwarden, 1Password, and Apple Advanced Data Protection make for their vaults, and we make it deliberately.
The full security whitepaper, with the cryptographic primitives named in the precise
vocabulary, will publish at launch. If you have questions before then, write to
security@afterward.care.